Customer scope summary
This summary is ours. Tenant: Northwind.
Add an action and it is written here, in our words.
Early access
Know what to do now, this week, and at 30, 60, and 90 days. Afigima AI is on your side of the rollout.
This tool only reads data and never makes changes. Sign in
For the customer
It will coach you on the questions to ask before you choose a partner, onboarding tips, things to avoid, and how to run or build your own checks.
Engineers on our team have delivered XSIAM onboarding. Their experience guides the advice in the guide.
We can advise you through the process without seeing your data or knowing exactly what you are working on. The health check is separate, and it only reads when you connect a key.
Know what you're paying for, track scope and progress yourself, and avoid paying for hours you don't need.
You are here
Level 2 of 5 · Visibility 45%
1. Foundation
88%
2. Visibility
45%
3. Detection
—
4. Response
—
5. Optimization
—
Areas
Agent Management
84%
Broker VMs
88%
Security Profiles
91%
Data Sources
45%
Before and after
Overall 65 now, about 94 after these actions.
Data Ingestion Health
About a dayConfirm metrics_source recorded byte volume by vendor, product, and collector type.
About 11 points.
Silent or Stale Sources
About a dayFlag sources whose last event is older than 24 hours and day-over-day volume drops.
About 10 points.
Parsing and Modeling Health
About a dayList raw datasets that still hold data, plus the health-domain issue count.
About 9 points.
You're at Level 1. These 3 things get you to Level 2.
1
2
3
4
5
Silent or Stale Sources
About a dayFlag sources whose last event is older than 24 hours and day-over-day volume drops.
Parsing and Modeling Health
About a dayList raw datasets that still hold data, plus the health-domain issue count.
Data Ingestion Health
About a dayConfirm metrics_source recorded byte volume by vendor, product, and collector type.
You're at Level 1. This area is in place.
1
2
3
4
5
You're at Level 1. This area is in place.
1
2
3
4
5
You're at Level 1. This area is in place.
1
2
3
4
5
This summary is ours. Tenant: Northwind.
Add an action and it is written here, in our words.
The challenge
Sources you count on are missing, or they have gone quiet.
Issues stay noisy, and tuning never quite finishes.
Onboarding stalls when the next action is not written down.
How it works
01
Add a Cortex API key. This tool only reads data and never makes changes.
02
Run the check. It reads ingestion, tuning, and the rest of the tenant.
03
Overview shows your maturity level and the area scores beside it.
04
Act on the three fixes to start with. The steps are written for the console.
What you get
Each level has its own score, grounded in cited best practice. Your goals come first.
1
The key works, and agents and brokers are reporting.
2
The data you count on is arriving and parsed.
3
Noise is named after that data is trustworthy.
4
Cases and playbooks follow detections you trust.
5
Automation and headroom, after response is real.
Foundation through Optimization. Each level has its own score.
Measured areas show a percent. An unmeasured area says Not scored yet.
Overview says what to do now, this week, and at 30, 60, and 90 days.
The console steps are written out. Get help fixing this sends a request to expert advisors.
Talk to an advisor after the check. The button in Overview is Get help fixing this.
Who it's for
The check includes AES only when it is already licensed. It does not ask you to add it.
A partner can help you size and price AES for your environment.
Trust
This tool only reads data and never makes changes.
The key is encrypted before it is stored. The portal shows the key ID, not the secret.
Independent educational tool. Not affiliated with or endorsed by Palo Alto Networks. Informational only, not professional advice.
About
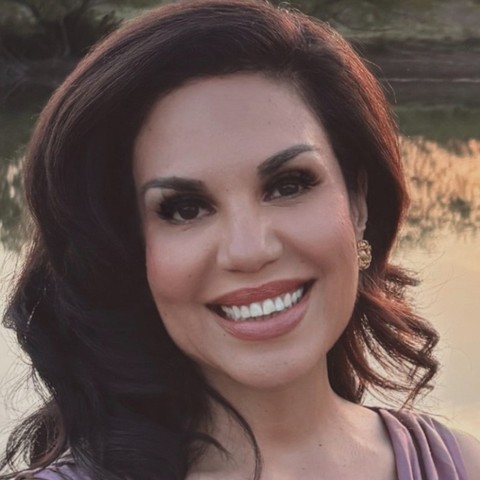
Christy Mendoza is the founder of Afigima Enterprises. Afigima AI is its service division, built to make complex security operations simpler. Cortex XSIAM is its first focus, with more services to come.
She built this site so security teams have one calm, clear place to see where their XSIAM setup stands and what to do next. Teams that are still onboarding get a guided path step by step. Teams already running XSIAM get their current setup gathered, scored against each maturity level, and turned into a short improvement plan. Behind it is a small team that shares her drive to make complex things simple.
Early access. Create an account, connect a Cortex API key, and you land on Overview.
No. This tool only reads data and never makes changes.
SOC leads, detection owners, leaders showing the value of the tenant, and partners running many tenants.
Independent educational tool. Not affiliated with or endorsed by Palo Alto Networks. Informational only, not professional advice.
Each level has its own score, grounded in cited best practice. Your goals come first.
Re-checks run weekly or every two weeks and show what moved. You can also run one whenever you want.
Yes. Delete the connection in the portal. The stored secret is removed with it.
This tool only reads data and never makes changes.